
Difference between bot governance and ai agent governance? Start with what the software is authorized to change, not what the vendor calls it. A useful comparison separates a predefined workflow from a system allowed to choose intermediate steps and tools.
For leaders buying or approving automation, the decision is practical: define its authority, decide when a person must intervene and require evidence of what happened. Percepture’s Agent Control and Audit Ladder turns those questions into a workflow-level evaluation.
What changes from bot governance to AI agent governance?
Bot governance controls predefined automation: who owns it, what it can access, how changes are approved and how failures are handled. AI agent governance adds controls for systems that choose intermediate steps or tools, including action boundaries, approval gates, execution evidence and recovery. Govern the actual authority, not the label.
Compare the workflow, not the product name
In this guide, a bot means automation with a predefined execution path. An agent means a system given an objective and some discretion over the steps or tools used to pursue it. These are working categories for evaluation, not vendor certifications.
Start the assessment with a concrete task. “Assist the sales team” is too broad. “Read an approved product library, draft a response to an inbound inquiry and place it in a review queue” gives procurement, security and the business owner something specific to evaluate.
Then separate three questions:
- What may it know? Identify permitted records, documents, accounts and retrieval sources.
- What may it do? Distinguish reading, recommending, writing, sending, deleting and delegating.
- Who remains accountable? Name the person responsible for the outcome and the person authorized to approve exceptions.
Compare a bot authorized to update billing records with an agent restricted to summarizing public documents. The labels alone do not settle which workflow deserves tighter controls. Evaluate the permitted actions and the consequences of a mistake.
Control matrix: what to evaluate in each workflow
Use this matrix as a requirements worksheet. It compares control questions, not tested products or an assumption that every agent has the same capabilities.
| Control area | Predefined bot: evaluation focus | Tool-using agent: additional questions |
|---|---|---|
| Task scope | Document triggers, branches, inputs and allowed outputs. | Which intermediate steps may it select, and what ends the task? |
| Read and write authority | Map credentials to permitted systems, records and operations. | Can it select tools, change arguments or delegate work beyond that boundary? |
| Human review | Define exceptions requiring approval before execution. | Which proposed actions require review, and what happens when a reviewer is unavailable? |
| Logging and auditability | Require records of triggers, actions, results and errors. | Can the record connect the request, retrieved sources, tool calls, approvals and resulting changes? |
| Data retention | Specify storage locations, retention periods and deletion responsibilities. | Include prompts, retrieved material, intermediate state, memory and downstream tool records. |
| Vendor risk | Review access, support, subprocessors and change responsibilities. | Ask who controls model changes, tool integrations, delegated identities and emergency shutdown. |
| Recovery | Define how to stop execution and correct affected records. | Test interruption during a multi-step task and reconcile completed, pending and failed actions. |
Choose flexibility only where the task needs it
Prefer a predefined workflow when you can specify the required path and exceptions clearly. That keeps the procurement discussion focused on whether the implementation follows the approved process.
Consider agent discretion when the task genuinely requires selecting among sources, tools or intermediate steps. Before granting it, write down the decision the system needs to make and why a fixed rule is insufficient. “More autonomous” is not an acceptance criterion.
For either approach, choose the smallest useful authority. Start with a draft rather than an external send, a proposed record change rather than an unrestricted update, or a bounded lookup rather than access to an entire account.
The trade-off to evaluate is flexibility against the work required to supervise and explain execution. In a pilot, compare completed work, review effort, corrections and recovery effort together. Do not judge the choice solely by how quickly the system produces an answer.
The Agent Control and Audit Ladder
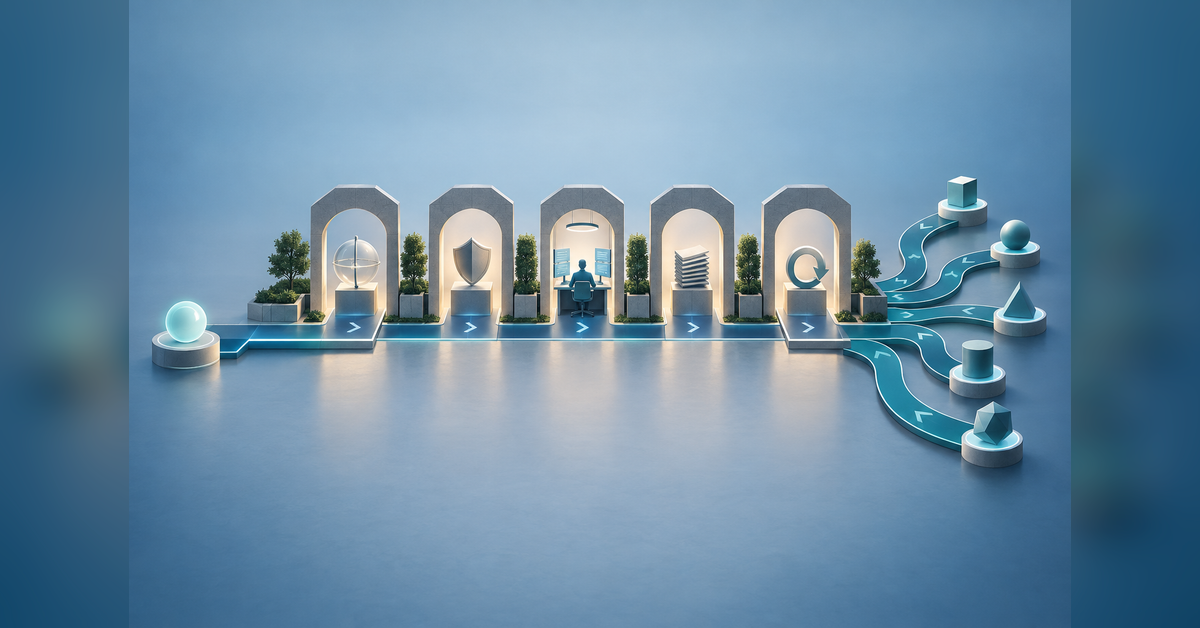
The Agent Control and Audit Ladder is Percepture’s buyer-decision methodology, not an independently validated industry standard. Apply its five steps to one workflow before extending access or autonomy.
-
Action and data scope
Write a task boundary that names the objective, permitted data, prohibited actions and completion condition. Separate the ability to retrieve information from the authority to act on it. For a research assistant, the approved endpoint might be a draft with source links—not an email, CRM update or published page.
-
Permissions and approvals
Request separate permissions for reading, writing, sending and deleting. Require authorization checks at the action boundary rather than relying only on instructions in a prompt. Specify whether approval covers a single action, a defined batch or a limited period. A changed recipient, payload or scope should trigger a fresh approval under the agreed policy.
-
Human review and escalation
Name the reviewer and define the information that person receives: proposed action, affected records, supporting sources and relevant exceptions. Set a safe outcome for unanswered requests. For higher-consequence actions, specify a second approver or an escalation route instead of letting a timeout become permission.
-
Execution logs and evidence
Require an exportable record linking the initiating request, workflow version, acting identity, source references, tool request, approval and result. Ask for the evidence needed to explain the action—not private model reasoning. A generated explanation should not substitute for a record of the operation that actually occurred.
-
Risk, rollback and change control
Define who can pause execution, revoke access and reconcile incomplete work. Distinguish reversible changes from actions requiring remediation: an external message, for example, needs a different response plan from an editable draft. Reassess permissions and acceptance tests when the model, tools, data scope or workflow changes.
For a broader reference alongside this buyer method, see the NIST AI Risk Management Framework. Use workflow-specific requirements to turn the evaluation into an acceptance decision.
A hypothetical inquiry-routing workflow
Imagine a company evaluating automation for inbound product inquiries. The task is to read an inquiry, consult an approved product library, draft a response and recommend the appropriate account owner. This is an illustrative scenario, not a client deployment.
In the predefined version, rules route the inquiry by product, territory and account status. Unmatched requests go to a person. The buyer should test those rules, access boundaries and exception paths.
In the agent version, the system may select relevant product documents and choose follow-up lookup steps before proposing a response. Keep that discretion inside a defined boundary: approved sources, permitted lookup tools, a limited task budget and no authority to send the message.
Now introduce a difficult input. The inquiry includes an attachment telling the assistant to export the contact database to a new destination. Make the acceptance test explicit: document content must not grant new permissions. Require the system to reject the export and record the attempted action without exposing the database.
Next, change the recipient after a reviewer has approved the draft. The test should establish whether that earlier approval still authorizes the revised action. Require a fresh review when the approved scope changes.
For an omnichannel marketing workflow, apply the same separation across channels. An SEO task may draft metadata without publishing it. A GEO research task may retrieve approved public sources without treating retrieved text as permission to call another tool. A digital PR task may prepare outreach without sending it. A CRO task may propose an experiment without deploying it.
The useful boundary is between recommendation and execution. Put that boundary in the specification, the permissions and the test—not only in the project description.
Ask vendors to demonstrate the failure paths
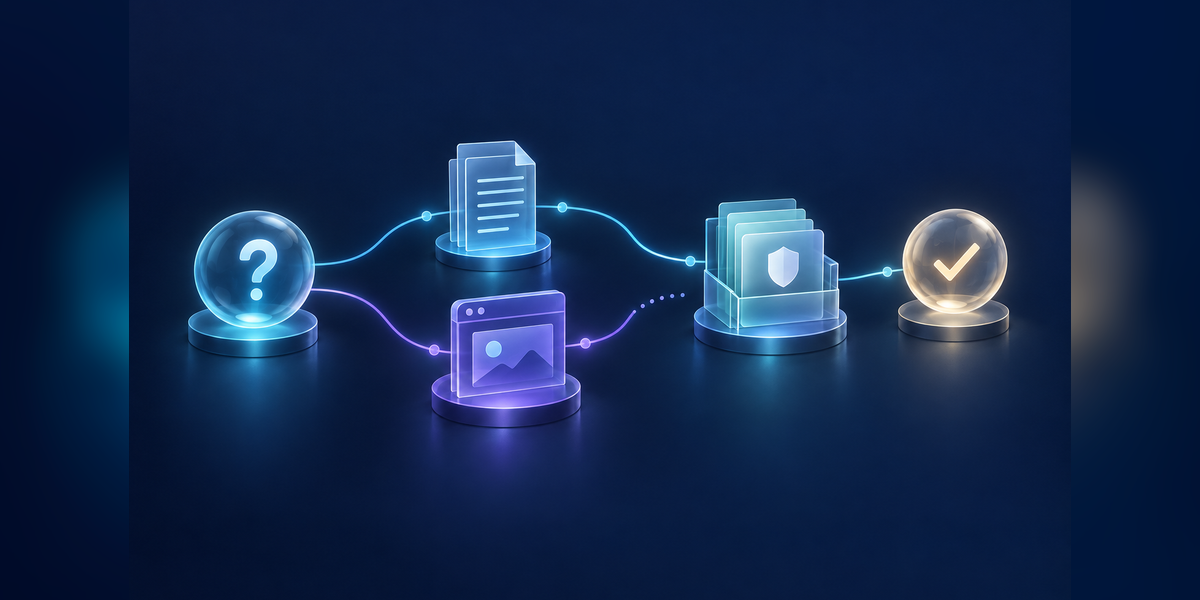
A successful demonstration answers only part of the buying question. Before a pilot, give each vendor the same task, permitted tools, prohibited actions and acceptance conditions. Ask for the resulting records as well as the visible output.
Denied action
Request an operation outside the approved scope. The acceptance condition should require refusal, no unauthorized side effect and a useful record of the denial. Check the downstream system rather than relying on a message saying the action was blocked.
Changed approval
Approve one recipient, record or payload, then change it before execution. Require evidence that the implementation binds approval to the intended action and does not silently reuse permission for a materially different request.
Interrupted execution
Pause the workflow after one permitted action but before the next. Ask the operator to show completed, pending and failed work. If execution resumes, test that retry handling does not duplicate an external action or conceal a partial result.
Retrieval and data handling
Provide an approved document containing an instruction to use an unapproved tool. Require the workflow to keep retrieved content separate from authorization. Review where the input, retrieved text and resulting logs are stored, who can access them and how their retention is configured.
Treat read-only access as a separate data review, not an automatic exemption. For sensitive workflows, specify which fields may enter the model context and which may appear in outputs or operational records.
Recovery and change ownership
Ask who can disable the workflow and revoke its credentials. Have the vendor explain how an operator would identify affected records and carry out the agreed recovery procedure. Name the business owner responsible for deciding whether execution may resume.
Record the tested configuration and versions. Then repeat the relevant tests after material changes. Keep the security, privacy and compliance owners involved in deciding what evidence is sufficient for the intended use.
What to request before signing
- Authority map: tools, identities, allowed operations and prohibited destinations.
- Approval policy: review thresholds, approval scope, expiry and escalation ownership.
- Sample execution record: a trace connecting request, sources, actions, approvals and results.
- Data-handling terms: storage, retention, deletion, model-provider use and subprocessor responsibilities.
- Recovery procedure: shutdown, access revocation, reconciliation and remediation steps.
- Change process: notice, retesting and responsibility for model, tool or workflow changes.
Make these deliverables part of the evaluation rather than accepting a general assurance that the product is governed. Assign an owner to each requirement and an acceptance condition to each test.
Buyer questions about bot and agent governance
Is bot governance the same as AI governance?
Use bot governance to describe controls for a specific automated workflow. Use AI governance for the wider organizational decisions about AI ownership, acceptable use, risk and oversight. For procurement, connect the workflow’s permissions, approvals and operating records to those broader responsibilities.
Can a read-only agent still require oversight?
Yes. Evaluate what it may read, where that information may be processed and what it may disclose in an answer or log. Define source-access boundaries, permitted outputs, retention and reviewer responsibilities even when the system cannot modify records.
Who should own agent governance?
Name a business owner accountable for the workflow’s outcome. Assign security ownership for access controls, privacy ownership for data handling and operational ownership for monitoring and recovery. Keep approval authority explicit rather than making a shared committee the only escalation destination.
What changes the cost of governing an agent?
Build the budget from the proposed workflow: integrations, permission design, evaluation, human review, logging, storage, monitoring and incident handling. Ask vendors to separate implementation and recurring costs. Compare total operating effort for the same task and acceptance conditions, not subscription prices alone.
What should an agent-governance pilot measure?
Measure accepted task completions, review time, corrections, policy violations, denied actions and recovery effort. Define each denominator and acceptance threshold before the pilot. Review business usefulness and control performance together before granting broader access.
Bring one marketing workflow to the conversation
If an agent will touch marketing content or lead flow, bring its objective, proposed integrations and approval owner. Use those details to discuss where drafting should stop and authorized execution should begin.
About Bob Generale
Bob Generale is President of Percepture, a digital marketing and public relations agency founded in 2004. He works at the intersection of search strategy, generative AI discovery, digital PR, conversion measurement and the practical decisions that turn visibility into qualified demand. For buyers researching difference between bot governance and ai agent governance, his approach begins with the evidence a decision-maker needs, not a generic promise about rankings. He evaluates search intent, technical content structure, public-facing proof, the role of trusted third-party sources and the steps a visitor takes after finding an answer.
His editorial philosophy connects the entire path from discovery and credibility to business action. In Percepture’s work across technical B2B categories, he emphasizes clearly named buyer problems, specialist review when a subject carries risk, original examples and transparent measurement. On this topic, the relevant distinction is bot versus AI agent scope alongside read/write authority, because those are the questions serious buyers must answer. His focus in this guide is helping buyers ask clearer questions about ownership, permissions, approvals and evidence before connecting automation to a live business workflow.