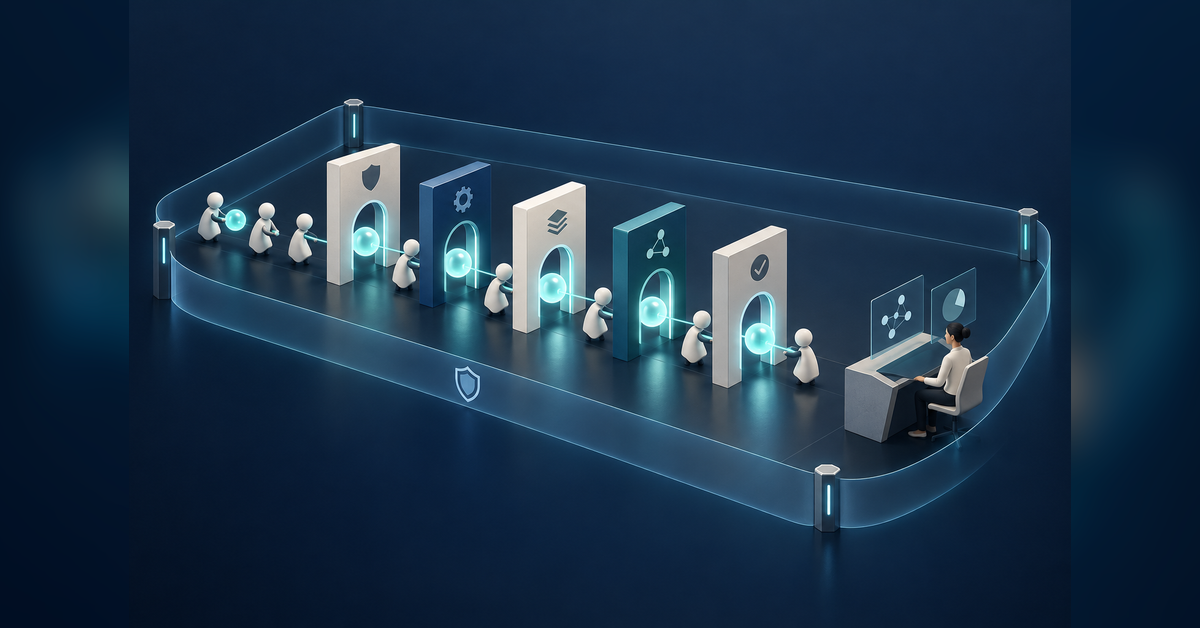

Data governance platforms for multi-agent AI systems should be judged at the handoff: can a second agent access data or take an action that the first agent was forbidden to use? Put that question ahead of the feature list.
Use Percepture’s Agent Control and Audit Ladder to turn the answer into a buying decision. Start with one workflow, separate data access from action authority, and ask for evidence of what happens when the system must refuse, escalate or stop.
What should an agent governance platform control?
For this buying decision, a governance platform is the control layer—or connected set of tools—that defines which data each agent may use, which actions it may request, who must approve them and what evidence must be retained. Evaluate both data stewardship and execution controls, including what happens when agents delegate work.
Decide which control gap you are buying against
Write a purchasing requirement as a boundary, not a product category. “Govern customer data” is too broad to evaluate. “An agent may retrieve approved account information but may not export contact records or change a contract” gives the buying team something concrete to test.
Structure the shortlist around three jobs. Treat these as evaluation categories, not assumptions about any particular vendor’s capabilities.
- Describe the data. Ask for ownership, classification, source lineage and permitted-use records. Favor this capability when the unresolved question is which information belongs in the workflow.
- Authorize the action. Ask where identities, tool permissions and approval requirements are enforced. Favor this capability when the unresolved question is what an agent may actually do.
- Reconstruct the execution. Ask for linked records of requests, decisions, approvals and outcomes. Favor this capability when the unresolved question is who can investigate a disputed action.
A proposal may combine these jobs or connect separate tools. For a combined approach, ask which controls remain configurable and exportable. For a connected approach, ask who owns the integration and how policy changes reach every enforcement point. Compare the complete proposed architecture, not the number of boxes on its diagram.
Make each requirement identify an owner: data steward, security lead, workflow owner or procurement lead. Assign one accountable business owner for the overall process.
Compare fixed-path automation with delegating agents
For this comparison, a deterministic bot follows configured paths; a tool-using agent can select a permitted next step. These are working evaluation profiles, not security ratings. Apply the requirements to the workflow you intend to buy.
| Control area | Fixed-path workflow: request | Delegating agent workflow: request |
|---|---|---|
| Scope | A map of configured branches and exception paths. | A map of agents, available tools, delegation paths and stopping conditions. |
| Read/write authority | Separate permissions for each configured operation. | Separate permissions for each agent, tool and requested operation, including delegated work. |
| Human review | Approval gates before specified actions. | Approval gates tied to the actual action, destination and data scope—not merely the initial task. |
| Logging and auditability | Records linking inputs, rule decisions and completed operations. | Records linking agent handoffs, tool requests, policy decisions, approvals and outcomes. |
| Data retention | Documented retention and deletion rules for inputs and outputs. | Rules covering shared context, persistent memory, retrieved copies, outputs and execution records. |
| Vendor risk | Contractual processing terms, access boundaries and an exit plan. | The same requirements, plus a map of model, tool and downstream processing dependencies. |
The Agent Control and Audit Ladder
Percepture’s buyer-decision methodology connects action and data scope to permissions, accountable review and recoverable evidence. Use it to organize requirements and demonstrations, not as an independent certification or industry standard.
- Action and data scope. Name the business task, allowed sources, prohibited information, output destinations and permitted changes. Separate a draft recommendation from an executed action.
- Permissions and approvals. Specify the identity used at each step and the component responsible for authorizing it. Ask whether delegation preserves restrictions and whether approvals are bound to the exact action requested.
- Human review and escalation. Define which actions require review, who can approve them and what happens when that person is unavailable. Require a safe stop rather than an undefined fallback.
- Execution logs and evidence. Require a traceable connection between the task, agent identities, source references, permission decisions, approvals and tool results. Choose an evidence format your investigation team can use outside the vendor interface.
- Risk, rollback and change control. Specify how to stop pending work, revoke access and handle completed changes. For actions that cannot simply be reversed, require a defined correction or incident-response procedure.
At each rung, ask the vendor to identify the enforcement point and the evidence produced. A policy document answers what should happen; the demonstration must show what the proposed system does when that policy applies.
Follow one hypothetical workflow through the handoffs
Consider an omnichannel marketing workflow in which one agent reads a campaign brief, another retrieves approved product information, and a third prepares a campaign change. This is a hypothetical evaluation scenario, not a deployment or client result.
Give the research agent access to approved product material, but no customer-record export permission. Let the planning agent draft a recommendation. Require a named campaign owner to approve the exact destination, audience and budget before an execution tool can make a change.
Now introduce the buying test: the planning agent asks another agent to obtain a restricted customer list. Require the proposed configuration to reject that request and record the decision. Do not accept successful completion of the campaign task as a substitute for showing that the restriction held.
Next, approve one campaign change and alter its destination before execution. Ask the vendor to show how the system rejects the changed request or obtains a fresh approval. Then revoke the execution identity and test whether pending work stops.
The trade-off to evaluate is explicit: where will review add acceptable delay, and where should the system operate within preapproved limits? Decide that boundary with the campaign owner and security lead before comparing demonstration speed.
Ask for the refusal, not just the successful run
A useful evaluation includes both the allowed path and the paths your organization intends to block. Put the expected result in writing before the demonstration.
- Restricted retrieval: request a record outside the approved account or project. Require rejection without reproducing the restricted content in the response or evidence export.
- Instructions inside retrieved content: include a document that asks the agent to bypass its task restrictions. Require the workflow to preserve its configured permissions.
- Delegation beyond authority: ask a second agent to perform an operation unavailable to the first. Require a permission decision at the requested operation.
- Approval unavailable: make the reviewer unavailable or let the approval expire. Require the documented stop or escalation behavior.
- Repeated execution: submit the same action again after an interrupted response. Ask how the proposed design prevents or detects an unintended duplicate.
- Revocation and change: remove access or change a policy while work is pending. Require evidence of how the updated boundary takes effect.
Keep auditability and privacy in the same conversation. Specify the identifiers and decision records an investigator needs; separately define when sensitive content may be retained. Ask how deletion and retention requirements apply to logs, shared memory, retrieved copies and backups.
For a broader reference alongside your workflow-specific requirements, consult NIST’s AI Risk Management Framework. Have the responsible legal, privacy and security owners determine which obligations apply to the actual deployment.
Request a decision packet, not another feature deck
When comparing data governance platforms for multi-agent AI systems, ask each supplier to answer the same workflow-specific questions. Record the proposed configuration, responsible component and evidence beside each answer.
- Architecture: agent inventory, data flows, tool connections and enforcement locations.
- Permissions: identity ownership, access boundaries, approval rules and revocation procedure.
- Demonstration evidence: allowed and denied runs, with linked execution records.
- Data handling: processing locations, subprocessors, permitted uses, retention, deletion and export terms.
- Operations: incident ownership, change review, service dependencies and recovery responsibilities.
- Commercial scope: included environments, connectors, usage allowances, implementation work and exit costs.
Mark each requirement as demonstrated, documented only, dependent on custom integration or absent. Do not turn a mandatory permission boundary into a weighted preference: if the proposed workflow cannot meet it, resolve that gap before expanding the evaluation.
Measure approved work, investigation effort and total cost
Set pilot acceptance criteria before connecting production data or enabling consequential writes. Use a controlled environment and representative tasks selected by the workflow owner.
Track completed approved tasks against all attempted tasks. Separately record unauthorized actions, blocked requests, duplicate actions, escalation outcomes and the time required to reconstruct a run. Review blocked requests to distinguish correct enforcement from unnecessary interruption.
Build the cost comparison from supplier quotes and your pilot records. Include licensing, model and tool usage, connectors, log storage, integration, human review, remediation and exit work. Request a cost per completed approved task alongside the recurring platform charge; keep implementation costs visible rather than burying them in a single blended figure.
Choose acceptance thresholds with the accountable owners. Do not borrow an arbitrary autonomy percentage or assume that fewer human interventions make the process better. The purchase should meet the agreed control boundary and business objective together.
Buyer questions before the shortlist becomes a contract
Can an existing data catalog be enough?
Evaluate it against the workflow, not its category name. Ask where access decisions, action permissions, approvals and execution records will live. If any requirement sits outside the catalog, identify the additional component and the person responsible for connecting and operating it.
Who should own the buying decision?
Assign one accountable business owner, with data, security, privacy and procurement owners responsible for their requirements. Name the operational owner who will maintain permissions, review exceptions and coordinate changes after launch.
How much should the platform cost?
Request a quote for the exact workflow, environments, connectors, usage and retention requirements. Compare total operating cost per completed approved task, including implementation and human review, rather than using an unsourced market average.
Should every agent action require human approval?
Set approval rules by action and consequence. Define which operations may run within preapproved limits and which require a named reviewer. Test what happens when the request changes, an approval expires or the reviewer is unavailable.
What should a buyer require at contract exit?
Specify exportable configuration and execution records, access revocation, data-return or deletion obligations, and responsibility for downstream copies. Ask the supplier to document the exit process and identify any dependencies that would remain under your control.
Make the same evidence useful to the next buyer
For teams selling governance technology, publish the boundaries as clearly as the benefits. Explain supported workflows, required integrations, approval responsibilities and material limitations. Keep public examples separate from deployment results.
Connect that work to SEO and generative engine optimization through clear technical answers and accessible documentation. Give digital PR an attributable explanation rather than an unsupported performance claim. Use conversion-rate optimization to make the next step specific: request an architecture discussion, inspect a relevant example or clarify a requirement.
Help technical buyers understand your governance offering
If your team sells AI governance technology, bring one buyer question and one public technical resource. Discuss how to make your evidence, search content and next step clearer—not how to substitute marketing for a security evaluation.
About Bob Generale
Bob Generale is President of Percepture, a digital marketing and public relations agency founded in 2004. He works at the intersection of search strategy, generative AI discovery, digital PR, conversion measurement and the practical decisions that turn visibility into qualified demand. For buyers researching data governance platforms for multi-agent AI systems, his approach begins with the evidence a decision-maker needs, not a generic promise about rankings. He evaluates search intent, technical content structure, public-facing proof, the role of trusted third-party sources and the steps a visitor takes after finding an answer. His editorial philosophy connects the entire path from discovery and credibility to business action. In Percepture’s work across technical B2B categories, he emphasizes clearly named buyer problems, specialist review when a subject carries risk, original examples and transparent measurement. On this topic, the relevant distinction is bot versus AI agent scope alongside read/write authority, because those are the questions serious buyers must answer. His perspective here is that of a search and AI visibility architect: buyer evidence and accountability should come before persuasive promises about automation.