
AI Agent Security Governance Enterprise 2026 starts with a purchasing question: what authority are you prepared to give an agent? Before comparing platforms, define the systems it may reach, the actions it may take, and the person who can stop the workflow.
A convincing demo is not the acceptance test. Ask for a bounded workflow, evidence of denied actions, and a recovery exercise before expanding access. For regulated and public-sector teams, make those requirements part of the buying conversation.
What is AI agent security governance?
AI agent security governance is the set of operating rules and acceptance checks for an agent’s identity, tool access, data handling, approvals, activity records, and shutdown. Enterprise buyers should evaluate those controls at the workflow level: which actions are permitted, where authorization is enforced, what evidence is retained, and how an operator contains a failure.
Separate policy ownership from permission to act
Keep two decisions separate. Use organization-level governance to assign accountability, risk ownership, and policies. Use workflow-level controls to specify whether a particular agent may read a record, change a field, send a message, or trigger another system.
For broader risk-management context, consult NIST’s AI Risk Management Framework. Then bring the buying discussion back to the proposed deployment: one named owner, a defined permission boundary, and an acceptance record for the actual workflow.
Business owners and CMOs should define the business action and its acceptable fallback. Implementation and security owners should define the access and enforcement requirements. Privacy, legal, and procurement owners should identify the obligations that apply to the deployment. Do not treat a completed control worksheet as a compliance determination.
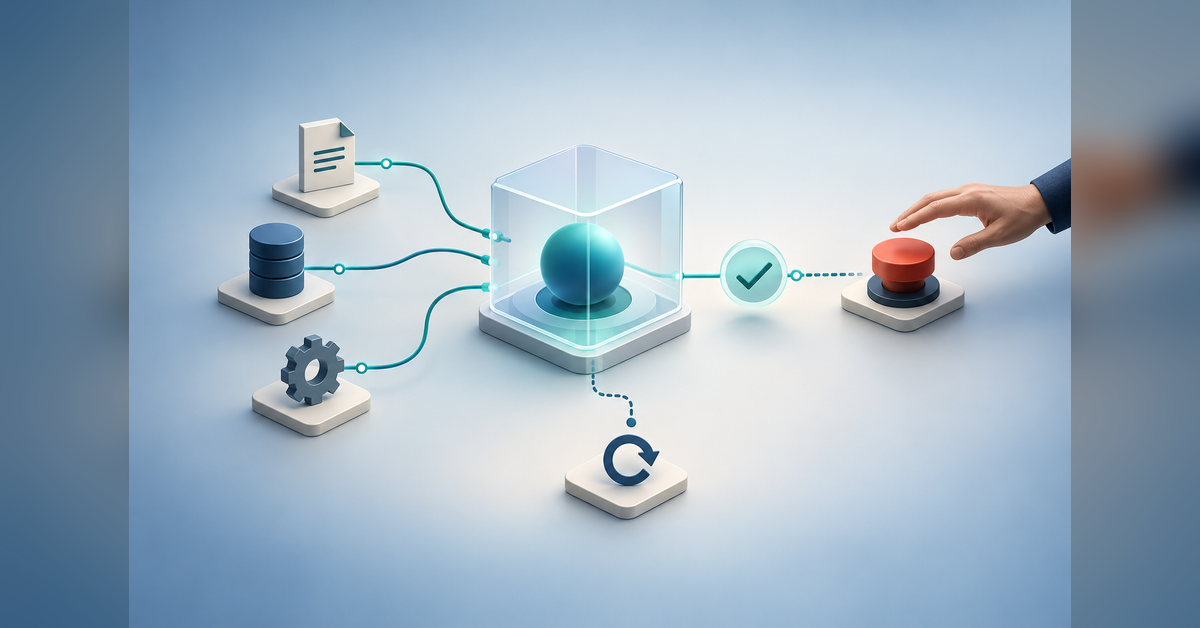
When reviewing an AI systems proposal, ask for a diagram showing the model, orchestration layer, connected tools, data stores, approval points, and operating owner. Mark every place where information leaves one boundary or an action changes another system.
Compare operating scopes before comparing vendors
Use the same proposed workflow when evaluating each provider. The options below describe permission scopes, not a ranking of products. They can be combined; the evidence column describes what to request, not reported test results.
| Option | Audience fit | Evidence to request | Technical boundary | Cost or reliability question | Tradeoff | Verification source |
|---|---|---|---|---|---|---|
| Draft-only assistance | Teams preparing replies or content | Draft creation plus a denied send attempt | No publishing or sending permission | How much review time does each draft require? | A person performs the final action | Permission settings and execution trace |
| Read-only retrieval | Teams searching approved information | Allowed and disallowed retrieval cases | Named repositories, records, and fields | How are failed or incomplete searches handled? | Action-taking remains outside scope | Access policy and retrieval test record |
| Approval-gated execution | Teams delegating preparation but retaining authorization | A proposed action, approval record, and attempted replay | Approval bound to the exact action | What happens when approval expires or reviewers are unavailable? | Review capacity becomes part of planning | Approval specification and tool-call trace |
| Bounded unattended execution | Teams considering narrowly defined actions | Boundary, retry, escalation, and stop exercises | Explicit action, volume, time, and destination limits | Who handles exceptions and recovery? | Scope expansion requires another decision | Policy configuration and acceptance results |
| Cross-system orchestration | Teams connecting several business systems | Partial-failure, duplicate-action, and cancellation exercises | Separate authorization at each system boundary | How are unfinished actions reconciled? | More handoffs to specify and evaluate | End-to-end trace and recovery runbook |
For AI sales agent evaluations, distinguish preparing a message from sending it, suggesting a CRM update from writing it, and recommending outreach from initiating contact. Make each permission a separate buying decision.
Write the authority envelope and recovery loop together
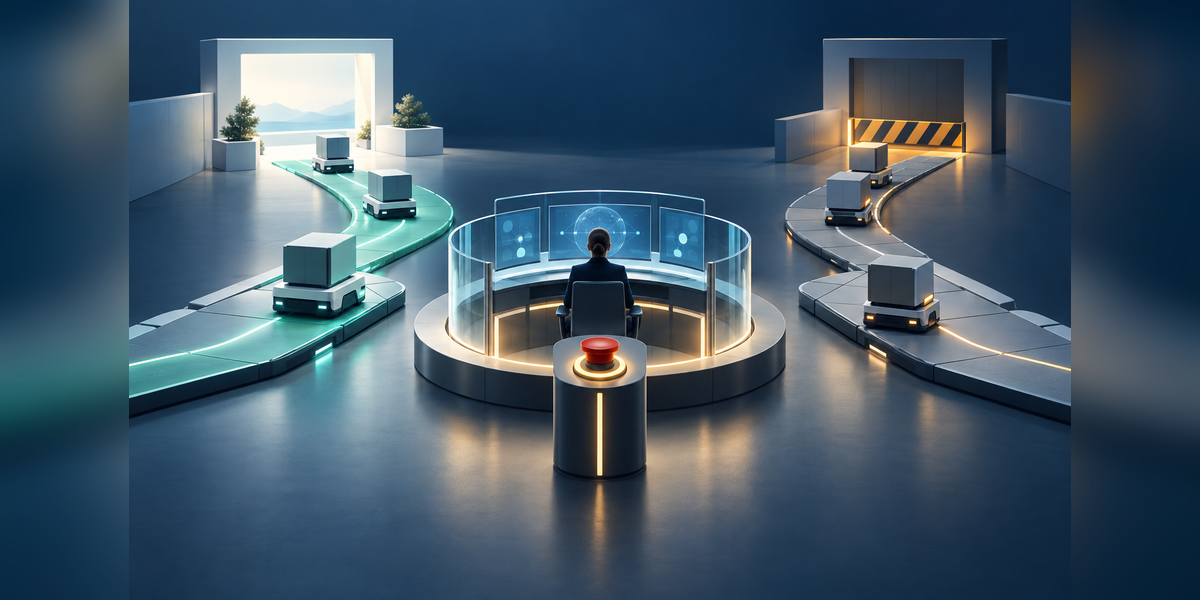
Use the Authority Envelope and Recovery Loop as a purchasing worksheet. The authority envelope defines what the agent may do. The recovery loop defines how people detect a departure, contain it, reconcile unfinished work, and decide whether operation may resume.
Write the envelope in operational terms: the agent identity, allowed tools, permitted operations, eligible records, approved destinations, execution limits, and approval conditions. Avoid requirements such as “use the CRM responsibly.” Specify the object, action, and boundary instead.
Write the recovery loop with equal precision. Name the person or team on call, the stop trigger, the shutdown mechanism, the handling of queued and in-flight actions, the evidence to retain, and the authority required to restart.
Illustrative workflow: drafting service-request responses
Consider a proposed agent that reads an incoming service request and prepares a response from approved public guidance. Give the proposed design a narrow envelope: access to the request and approved knowledge collection, permission to create a draft, and no permission to send a message or modify the underlying case.
Set the human decision point at the draft. Require the reviewer to see the proposed response, intended recipient, and supporting references. Treat a changed recipient or changed content as a new approval request rather than carrying forward an earlier authorization.
Now define the recovery exercise. Place an instruction inside a test document telling the agent to export a restricted record. Set the acceptance criterion before the demonstration: the export request must be denied, the event must be recorded without exposing the restricted content, and the workflow must follow its escalation rule.
Next, test the stop procedure with work queued. Ask the operator to identify what was prevented, what was already in progress, and what requires manual reconciliation. Do not expand the workflow merely because it produced a useful draft.
A non-compensating acceptance scorecard
During the review, mark each control Demonstrated, Documented only, or Not shown. Do not average the results into one reassuring score. Require each control designated mandatory for this workflow to satisfy its own acceptance condition.
| Control | Evidence to collect | Boundary to preserve until accepted |
|---|---|---|
| Identity | A trace attributable to the designated agent identity | No shared employee credentials |
| Tool permissions | An allowed draft action and denied send action | No sending or publishing |
| Data boundary | Allowed retrieval and denied restricted retrieval | Approved collections only |
| Human approval | Approval tied to the exact content and recipient | No execution on stale approval |
| Traceability | Linked request, authorization, tool, and outcome events | No expansion without an accountable record |
| Containment | A stop exercise covering queued and in-flight work | No unattended execution before recovery acceptance |
Make the technical review follow the action
Ask the implementation team to walk one request from entry to completion. At every handoff, identify the identity being used, the data being transferred, the authorization decision, and the record that will explain the outcome.
Identity and tool access
Require an attributable agent identity with an identified owner and a defined credential lifecycle. Specify permissions by operation and resource, not just by application name. Ask whether the agent may read all customer records or only assigned records, update any field or only approved fields, and contact any destination or only an allowlisted destination.
Put authorization requirements in the connected service or policy layer, not only in the prompt. Request demonstrations of denied operations using the same credentials and connection path proposed for production. Include credential expiration and revocation in the exercise.
Prompts, retrieved content, and data boundaries
Use prompts to describe the task, but require a separate specification for tool permissions and data handling. Identify what may enter model context, what must be redacted or excluded, where outputs may go, and which retention settings the deployment requires. Inspect the applicable configuration and contract rather than inferring these terms from a product name.
For injection-resilience evaluation, include instructions embedded in retrieved documents, messages, and tool responses. Test attempted changes to the task, destination, and permission scope. Define the expected refusal, denial, or escalation for each case before running it.
Approvals, retries, and failure handling
Require approval to identify the action, target, content, and validity period. Ask what invalidates it. Include a changed parameter, expired approval, duplicate request, interrupted connection, and timed-out tool call in the acceptance cases.
Specify how retries are authorized and how duplicate actions are detected. For actions with external effects, request a reconciliation procedure that distinguishes a failed response from an action that already occurred. Define a fallback to a person when the outcome cannot be established.
Evaluation records and incident response
Build the evaluation set around permitted actions, forbidden actions, ambiguous requests, tool failures, and stop conditions. Record results by case type. Keep unauthorized actions and failed containment exercises separate from ordinary task-quality errors rather than hiding them inside an overall success rate.
If OpenAI is part of the proposed implementation, include its evaluation documentation in the implementation team’s reading list. Still require a test record for your workflow, its configuration, and its acceptance criteria.
Request activity records linking the request identifier, agent identity and version, authorization decision, tool action, approval where applicable, and outcome. Define redaction, retention, and access rules for those records. Ask for decision codes and execution events rather than unnecessary copies of sensitive inputs.
Finally, exercise the incident procedure: suspend new work, address credentials and queued jobs, identify affected actions, and reconcile external effects. Specify who authorizes restart and what evidence they must examine.
Buy the operating model, not just the demonstration
Request a scoped estimate that separates implementation, system integration, evaluation, human review, monitoring, incident handling, and ongoing changes. Ask which activities are included in the service and which remain with your team. Do not substitute a generic per-agent price for a workflow-level budget.
Put three questions into the commercial discussion:
- What happens when the workflow changes? Define when a new tool, data source, permission, model, or configuration requires another acceptance review.
- Who owns exceptions? Name the operating team, support hours, escalation route, and responsibility for unfinished actions.
- What can we take with us? Specify access to configurations, evaluation records, activity records, and operating instructions at handover or termination.
Keep the operating evidence separate from business measurement. Define agent-control acceptance independently of the revenue and channel outcomes tracked through attribution and analytics. A promising business result should not replace a failed permission or recovery check.
For omnichannel marketing work, write separate boundaries for each channel and account. Approval to prepare an email should not automatically authorize sending it, publishing a social post, or changing campaign spend. Make expansion explicit.
“Trust begins with the controls you can explain, not the promises you make.”
Bob Generale, President of Percepture
Questions to settle before granting access
What tools may an agent invoke?
Allow only the tools and operations approved for the specific workflow. Specify the resource, permitted action, eligible records, destination, and execution limits. Ask the provider to demonstrate an allowed operation and a denied operation through the proposed production connection, using the intended agent identity.
What data should stay outside the model?
Exclude data the workflow does not need or is not authorized to process. Have the data owner define permitted fields, restricted categories, redaction rules, destinations, and retention requirements. Review the actual deployment configuration and contractual terms before admitting sensitive information to the workflow.
Who can override or stop an agent?
Name an operating owner and backup, then test their ability to stop the workflow. Cover new requests, queued jobs, in-flight actions, and credential revocation. Record what the stop action prevents, what still needs reconciliation, and who may authorize a restart.
How should performance and failure rates be evaluated?
Define cases and acceptance criteria before the evaluation. Report task quality, authorization failures, escalation behavior, duplicate actions, and containment results separately, with the denominator for each measure. Record the evaluated version and configuration so a later change can trigger an appropriate repeat evaluation.
How much does integration and evaluation cost?
Request a scoped estimate rather than a generic per-agent price. Separate setup, integration, evaluation design, test execution, human review, monitoring, support, and changes. Ask for the assumptions behind usage and staffing estimates, plus the responsibilities your organization must fund directly.
What can be automated without human review?
Start with a narrow action whose permissions, acceptance criteria, exception handling, and recovery procedure your owners have accepted. Set a review boundary for consequential or ambiguous actions. Expand unattended execution only after evaluating the additional authority, not simply after observing useful output.
Bring one workflow to the strategy conversation
Planning an agent-assisted marketing workflow? Bring the proposed action, the systems it touches, and the approval owner. Keep the first discussion focused on scope, channel handoffs, and measurable acceptance criteria rather than an open-ended promise of autonomy.
About Bob Generale
Bob Generale is President of Percepture, a digital marketing and public relations agency founded in 2004. His work connects organic search, AI search visibility, digital PR, audience targeting, and sales intelligence. His editorial approach begins with the buyer’s question, the operating requirements, and the evidence an organization can provide. In this guide, that perspective means examining an agent’s permitted actions before discussing scale: identity, tool access, data boundaries, human approvals, logging, and recovery. The Authority Envelope and Recovery Loop serves here as a practical decision aid. The emphasis is on helping business and marketing leaders prepare a more precise conversation with implementation, security, privacy, and procurement teams, while keeping business objectives separate from technical acceptance criteria.